TECHNOLOGY
The engineering
behind HOICROM.
Architecture, security and privacy, explained clearly: this is what stands behind every decision the system makes.
For those who decide and those who review:from the big picture down to the last protocol.
EVERYTHING RUNS ON HOICROM CORE
- Identity
- Permissions
- Policies
- Risk
- Decision
- Human approval
- Audit
ARCHITECTURE AND STACK
One shared technology base.
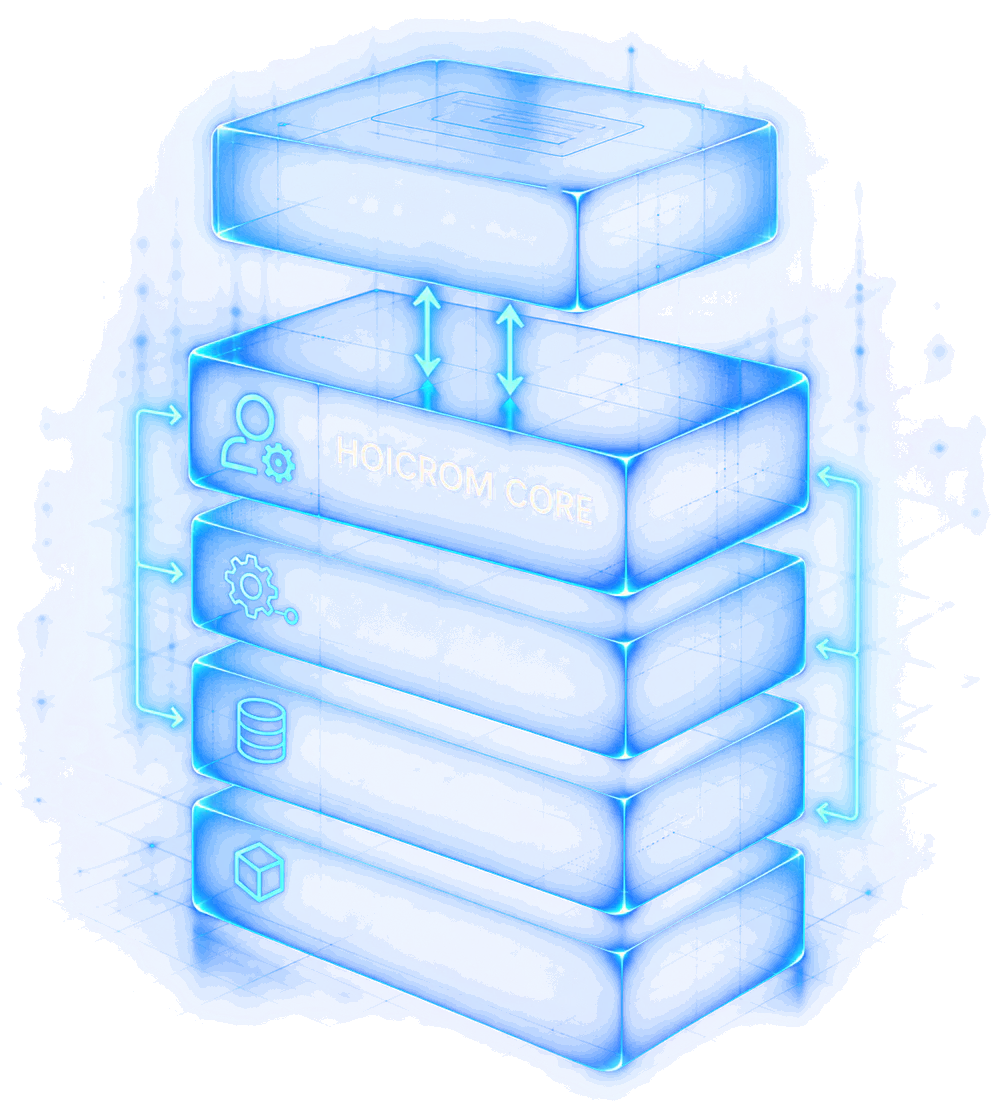
HOICROM Core, SECURE and BUILD share the same layers. This is what sits in each one.
- Applications and products layerWhere SECURE and BUILD run, over encrypted APIs.
- TypeScript
- Python
- Node.js
- REST
- GraphQL
- TLS 1.3
- HOICROM CoreWho you are and what you can do: identity and access.
- OAuth 2.0
- OpenID Connect
- SAML 2.0
- JWT
- Processing servicesThey analyse AI activity in real time.
- Apache Kafka
- Webhooks HMAC-SHA256
- Data layerEncrypted and isolated per customer.
- PostgreSQL
- Redis
- Container infrastructureAutomatic scaling and deployment as code.
- Docker
- Kubernetes
- Terraform
HOICROM SECURE
The technology of the three layers.
Prevention, detection and control, on the same Core.
Seatbelt
PreventionWhere it acts
- WebExtensions
- Endpoint agent
- HTTP(S) proxy
What it detects
- IBAN · ISO 13616
- Luhn
- DNI/NIE
- NER
- OCR
- Document classification
How it protects
- Pseudonymisation
- FPE · NIST SP 800-38G
Radar
DetectionCollects
- OpenTelemetry (OTLP)
- Apache Kafka
- ClickHouse
Detects
- Sigma rules
- scikit-learn
- PyTorch
Tags
- MITRE ATLAS
- OWASP Top 10 for LLM
Alerts your SIEM
- Syslog (RFC 5424)
- CEF
- Signed webhooks
Airbag
ControlDecides
- Open Policy Agent
- Rego
- Allow · Review · Block
Intercepts
- MCP
- REST
- gRPC
Approves
- WebAuthn / FIDO2
- Webhooks
Connects to your systems
- REST
- OAuth 2.0
- SCIM 2.0
- SAML 2.0 / OIDC
- SMTP / IMAP
HOICROM BUILD
The technology of the agents.
How they connect, run and get tested.
- Tool connection
- Model Context Protocol
- Orchestration
- LangGraph
- LangChain
- Durable execution
- Temporal
- Tool calls
- Function calling
- JSON Schema
- Memory
- pgvector
- PostgreSQL
- Isolation
- Docker
- Firecracker
- gVisor
- Per-action permissions
- OAuth 2.0
- Testing
- Evals
- Regression
SECURITY AND PRIVACY
Your data, under control.
How we protect the system, and what we do, and don't do, with your data.
Security
- EncryptionTLS 1.3 + HSTS · AES-256-GCM · Argon2
- Strong authenticationMFA: TOTP (RFC 6238) · WebAuthn/FIDO2
- Access controlRBAC with least privilege · ABAC
- Immutable auditHash-chained log across Secure and Build
- MonitoringReal-time event correlation (SIEM)
- Secure codeSAST · SCA · DAST + CI/CD checks on every deployment
Privacy and data
- PseudonymisationSensitive data is tokenised before it reaches the AI.
- Retention and deletionConfigurable: automatic or on request.
- Data residencyEU by default [CONFIRM].
- GDPRWith a Data Protection Officer [CONFIRM].
- ISO/IEC 27001Aligned with the standard; certification [CONFIRM].
- No training on your dataNever used to train third-party models.
DEPLOYMENT
Choose how you run it.
The same stack in all three models.
- SaaS · Managed by HOICROMMulti-tenant on Kubernetes. Quick to start.
- Enterprise · In your cloud or on your serversInstalled in your environment, with the same stack and under your control.
- Hybrid · Part yours, part managedCombines your environment with services managed by HOICROM.
Want to see how it fits your company?
Talk to an engineer or request a demo.