Hoicrom

FREQUENTLY ASKED QUESTIONS

All you need to know
about HOICROM.

We answer the most common questions about how we protect, control and build AI for companies.

30 questions

01. About HOICROM

What HOICROM is, how it works and what makes it different.

  • What is HOICROM?

    HOICROM is the security layer between AI and your company. It lets you use AI with confidence: we see what it does, we stop data from leaking and we decide how far each agent can act, always with people in charge.

    It has two lines: Secure, to protect the AI you already use, and Build, to build agents and automations with security built in.

  • What is the difference between Secure and Build?

    Secure protects the AI you already use: it gives visibility, prevents data leaks and controls what agents can do.

    Build is for creating something new: we design, build and integrate agents and automations that are born under HOICROM's control. They share the same security base, and you can use one, the other or both.

  • What is HOICROM Core?

    It is the common base of Secure and Build, the engine that decides. It brings together identity and permissions, policies and rules, risk assessment, the decision (allow, review or block), human approval and the audit of everything that happens.

    It is not sold separately: it comes inside each product.

  • Is HOICROM a traditional cybersecurity tool?

    No. HOICROM does not replace the security tools you already have: it adds a layer designed specifically for AI, something classic systems do not cover: what data reaches it, what an agent does and how far it can act.

    It works on top of your current security, not instead of it.

  • What kind of companies is HOICROM for?

    For any company that already uses AI, or wants to, with access to its data or its systems.

    There is a SaaS model, designed to start quickly (for example, in small and medium companies), and an Enterprise model for more demanding environments, which can be installed in your cloud or on your own servers.
02. HOICROM Secure

How we protect and control the AI you already use in your company.

  • What does Radar do?

    Radar detects. It watches the activity of AI and connected systems in real time, identifies anomalous behaviour, improper access and threats, investigates what happened and why it is suspicious, and proposes the response.

    It is the main layer of Secure: it connects in a few clicks and starts in read-only mode.

  • What does Seatbelt do?

    Seatbelt prevents. It acts right where your employees and agents use AI: it controls which AI tools can be used, detects and blocks the sending of sensitive data (personal data, documents, code…), anonymises it when needed and applies your policies by role, department or agent.

    That way your data stays in its seat.

  • What does Airbag do?

    Airbag protects at the moment an AI or an agent wants to do something. It assesses the risk of each action before it runs, checks it against your rules and decides: allow it, send it to human review or block it.

    That way you decide how far each agent can act, and everything is recorded.

  • Do I have to sign up for all three layers?

    No. Each layer works on its own: you can start with the one you need most, combine several or deploy the complete system.

    If you use them together they coordinate: Radar detects and proposes, Airbag checks the response against your rules and applies it, and Seatbelt looks after your data before it leaves.

  • What kind of risks does it detect?

    The ones that appear when AI touches your data and your systems: leaks of sensitive information to external tools, unauthorised AI use, access to data that is not allowed, mass downloads, anomalous query patterns and agent actions that go outside your rules.

    Every alert comes with context so you know what happened and what to do.

03. HOICROM Build

How we build agents and automations with built-in security.

  • What kind of agents can HOICROM build?

    Agents and automations tailored to your operation: customer service, internal operations, data analysis and reports, automations that connect systems and specific solutions we define with you.

    All of them are born with HOICROM's security built in.

  • Can an agent connect to our systems?

    Yes, that is the idea: a useful agent works where the process happens. We connect it to your systems through APIs, MCP and defined tools, and every connection has its permissions: the agent can only do what you have authorised.

  • Can an agent carry out actions on its own?

    Yes, within the limits you set. Low-risk actions run on their own, sensitive ones wait for a person's approval and those outside your rules are blocked.

    You decide how much autonomy each agent has.

  • How is what an agent does controlled?

    With the same security base as HOICROM Core: identity and permissions (who can do what), policies and rules, risk assessment of every action, human approval when you decide it and full audit.

    In addition, each agent runs isolated, so its actions do not reach where they should not.

  • How long does it take to deploy an agent?

    It depends on the goal, the systems involved and the actions the agent can run. We start by understanding your process, design the agent, connect it and take it to production gradually.

    The specific timeframes are agreed with you once we know your case. [CONFIRM indicative timeframes]

04. Security and privacy

How we protect your data and guarantee safe use of AI.

  • Where is the data stored?

    On containerised cloud infrastructure, with databases that are encrypted and logically isolated per customer. If you need everything to stay in your own environment, the Enterprise model is installed in your cloud or on your own servers.

    The exact location of the data is defined with you (the EU by default). [CONFIRM data residency]

  • Is my company's data used to train third-party models?

    No. Your company's data is never used to train third-party models.

    In addition, sensitive data is pseudonymised (replaced by markers) before it reaches the AI.

  • Can HOICROM see all of my company's data?

    No. HOICROM does not read your whole company: Seatbelt acts only at the point where the AI is used, and Radar analyses the activity of the systems you connect.

    We work with least privilege —only what is necessary is accessed— and you can configure how long each piece of data is kept and when it is deleted.

  • Can a person approve the important actions?

    Yes. When an action is sensitive, the system does not run it: it sends it to review and waits for a person to approve or reject it.

    That approval is confirmed with strong authentication (for example, WebAuthn/FIDO2) and is recorded.

  • Is what the AI does recorded?

    Yes. Every decision and every action is saved in an immutable, hash-chained audit log, in both Secure and Build.

    That way you can know what the AI did, when, why it was allowed or blocked and who approved it.

05. Integration and deployment

How HOICROM integrates with your systems and what deployment options exist.

  • Do we have to change our current systems?

    No. HOICROM connects to what you already use through open standards (REST APIs, OAuth 2.0, SCIM, SAML/OIDC or SMTP/IMAP, among others) and does not replace your current security: it complements it for the AI layer.

  • Which systems can be integrated?

    ERP, CRM, email, files, accounts and applications, plus any AI you use: HOICROM works whatever the tool or the provider.

    If you use something less common, we will look at it with you.

  • How can HOICROM be deployed?

    In three ways, with the same technology stack: SaaS (managed by HOICROM, to start quickly), Enterprise (installed in your cloud or on your servers, under your control) and hybrid (part yours, part managed by us).

  • Do we need to install software on the computers?

    It depends on the layer. Radar connects to your systems and Airbag works with your rules, with nothing to install on each computer.

    Seatbelt acts where your employees use AI, so it normally starts with a browser extension on their computers (depending on your environment, it can also be a light agent or a gateway).

  • What support do you offer during implementation?

    We go with you throughout the process: we understand your environment, connect HOICROM to your systems, start in a safe mode before activating anything and adjust the rules with you.

    Later support and response times are agreed in each project. [CONFIRM support levels]

06. Company and project

Information about the company, the team and the recognition received.

  • Who is behind HOICROM?

    HOICROM was founded by Alejandro Mosquera Cardeso, its sole founder, aged 22.

    It was born from his experience building Chronetic, a conversational AI technology company for businesses: when deploying AI agents in real environments he saw that giving them access to systems, data and processes creates a new challenge —controlling what the AI can do— and he created HOICROM to solve it.

  • What is the Best Emerging Business Project award?

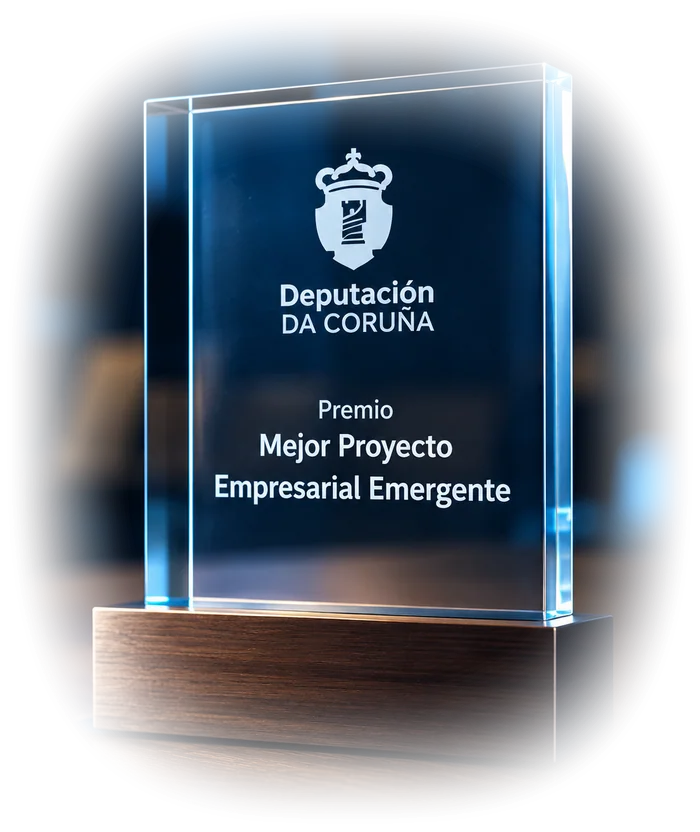
    It is the recognition we received from the province of A Coruña (Deputación da Coruña) as the Best Emerging Business Project: an award for our work, effort and vision for the future.

    We have also been selected among the 144 most innovative startups in the world to compete in the WMF finals in Bologna 2027 and fight for a place at the Startup World Cup, in San Francisco.

  • Which sectors do you work in?

    HOICROM is not designed for a single sector: it serves any company that uses AI with access to its data and systems.

    What changes from one case to another is which systems it has, what data it handles and which AI it uses, and that is why we always start by understanding yours.

  • Can we start with just one part of HOICROM?

    Yes. You can start with just Secure or just Build, and even with a single one of its layers —for example, Radar to see what is going on or Seatbelt to stop data leaks— and expand when you need to.

    They all share the same base, so growing does not mean starting over.

  • How can we work together?

    Write to us and tell us what you want to do with AI. You will talk to an expert, we will understand your case and suggest where to start: protecting the AI you already use with Secure, building an agent with Build, or both.

STILL HAVE DOUBTS?

Let's talk about your case.

Tell us what you want to do with AI and we will explain how HOICROM could fit in your company.

Talk to an expert